30 Blockchain Limitations for IoT
More
Depth: Practitioner
Progress saves as you read. Mark sections complete as you go; your progress appears in the sidebar.
30.1 Start With the Stress Test
This section: Start With the Stress Test — Picture several buildings sharing energy totals from their meters.
Keep Fast Work Outside the Shared Record
Picture several buildings sharing energy totals from their meters. Telemetry means readings and status sent from equipment for remote use. Latency means the time from an event to the result that matters. A gateway is a local device or service that joins equipment to wider systems. A shared ledger may help the owners check a later total, but it should not become the path for every reading or live charger action.
Write the boundary before choosing a ledger. Name the parties, raw store, local control, summary, time window, correction rule, private fields, signer, outage store, shared proof, and review owner.
Test a full day of readings, a missing meter, a late batch, a wrong calibration, a duplicate, loss of the ledger, loss of a gateway, a key change, and a later proof replay. Check that chargers remain safe and raw data can be corrected while the shared record keeps the accepted history.
Keep immediate alerts and control at the device or site. A record accepted by several parties can support later trust, but it is not a safe clock for a physical action.
This opening does not approve or reject every ledger. Practitioner builds the placement and governance record. Under the Hood examines load, ordering, finality, privacy, membership, outages, corrections, and how off-ledger evidence is checked again.
Use a small release drill. Make one accepted period, one late period, one corrected period, and one period made while the shared service is down. Keep the raw readings off the ledger. Rebuild each summary from the source store and compare its proof with the shared record.
The site should keep working through the drill. Staff should see which proof is delayed, which value changed, who accepted the change, and when the shared history caught up. Repeat the drill after a meter, signer, participant, rule, or storage form changes.
Close with a plain fit check. Does each shared item need more than one party to check it? Can the site work while the shared service is down? Can a wrong source value be fixed off the ledger? Can a new reviewer rebuild the proof? If any answer is no, move that job out or narrow the claim.
Blockchain limitations become visible when the IoT workload is made concrete: transaction rate, device resources, latency, privacy, correction, governance, and outage behavior all collide with the ledger promise.
Start simple: stress one proposed ledger record before approving the architecture. If the record cannot meet volume, timing, privacy, and recovery needs, the implementation choice has already failed.
30.2 Why Limitations Matter
This section: Why Limitations Matter — Blockchain can add value when several parties need a shared evidence history.
Blockchain can add value when several parties need a shared evidence history. It can also add avoidable fragility when it is used as a telemetry store, a control path, a device-security layer, or a substitute for governance.
This chapter stress-tests a proposed IoT ledger design before implementation. The goal is not to reject every ledger. The goal is to identify which parts of the system belong on ledger, which parts belong in normal IoT infrastructure, and which operating responsibilities must be accepted before deployment.
Before accepting a proposed ledger record, use Figure 30.1 to test it against six pressures that can narrow or reject the design.
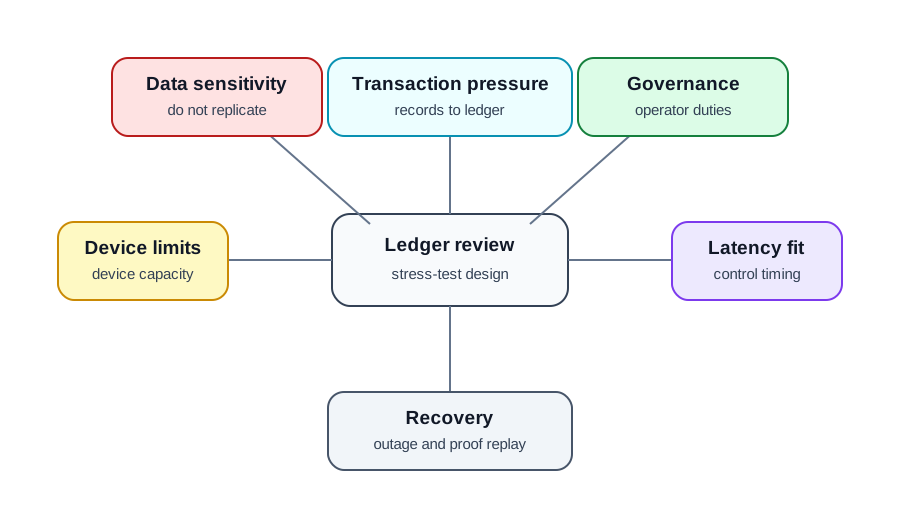
Begin Figure 30.1 with event volume: ask what reaches the ledger if every device event becomes a record. Then check device resources and control timing, which often push validation state and immediate action back to gateways or edge services. Sensitive raw data creates a separate placement limit. Governance names who may write, read, validate, and change the rules. Recovery closes the review by recomputing a stored fingerprint after an outage and comparing it with the ledger record. If any gate lacks a workable answer, move that job out of the ledger path or narrow the claim.
30.3 Learning Objectives
This section: Learning Objectives
By the end of this chapter, you will be able to:
- Identify where blockchain creates pressure in an IoT architecture.
- Separate raw telemetry and control paths from durable ledger evidence.
- Explain why constrained devices usually need gateway-mediated ledger access.
- Evaluate latency, storage, privacy, governance, and recovery risks.
- Prepare implementation-readiness evidence before approving a ledger design.
30.4 Quick Check: Meter Ledger Stress Test
This section: Quick Check: Meter Ledger Stress Test
Key Concepts
This section: Key Concepts
- Transaction pressure: The event volume that would reach the ledger if every device event became a ledger record.
- Resource boundary: The line between constrained devices and gateways or services that can handle ledger duties.
- Finality delay: The time between submitting a record and treating it as settled enough for the architecture.
- Data placement: The decision about what stays in operational storage and what becomes shared ledger evidence.
- Privacy exposure: The risk created when sensitive or correctable data is replicated to multiple parties.
- Governance burden: The work of admitting participants, changing rules, operating validators, and recovering from failures.
- Proof replay: A later review that recomputes a stored fingerprint and compares it with the ledger record.
30.5 Limitation 1: Transaction Pressure
This section: Limitation 1: Transaction Pressure — IoT systems can generate many events.
IoT systems can generate many events. A ledger should not receive every reading, log line, file, or diagnostic message. If the proposed design writes raw telemetry directly to a shared history, the design is probably using the ledger for the wrong job.
Sort the event stream in three groups:
| Event group | Typical handling | Why |
|---|---|---|
| Raw readings | Operational telemetry store | High volume, query-heavy, may need cleanup or recalculation |
| Local control events | Device, gateway, or edge service | Needs predictable response and clear safety behavior |
| Shared evidence | Ledger or signed audit record | Durable facts several parties must verify later |
Good ledger candidates are compact: custody handoff, meter period summary, device identity action, maintenance attestation, exception summary, and batch fingerprint. Poor candidates are high-frequency raw readings and anything that must drive immediate control.
Use Figure 30.2 to decide which high-volume records stay in operational storage and which compact facts need shared verification.
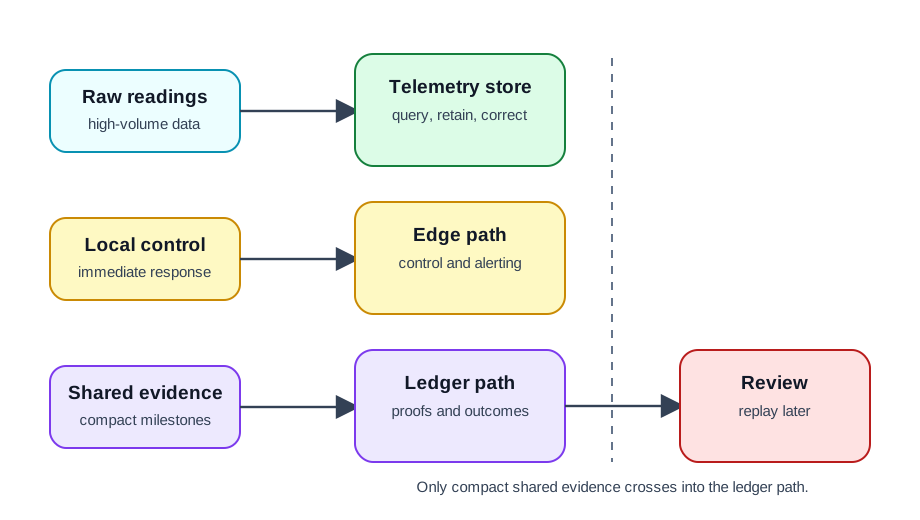
Start with the event group in Figure 30.2. Raw readings are high-volume and query-heavy, so the telemetry store keeps them where operators can retain, correct, and inspect them. Local control events stay with devices, gateways, or edge services because their response must remain predictable. Only compact candidates cross into the ledger path: a meter-period summary, an exception summary, or a batch fingerprint. Those records are useful when several parties must verify durable facts later. This placement reduces transaction pressure without discarding the off-ledger evidence needed to explain how a compact record was formed.
30.6 Limitation 2: Device Resource Boundaries
This section: Limitation 2: Device Resource Boundaries — Constrained devices are not good ledger participants.
Constrained devices are not good ledger participants. They may be able to sign a local event, but they should not be expected to store a ledger history, maintain validator state, communicate with every participant, or recover from ledger-level failures.
Use this boundary instead:
- The device observes and signs an event appropriate to its hardware.
- The gateway validates local context and buffers during outages.
- The gateway or service batches records and submits compact evidence.
- The ledger network accepts the record according to agreed rules.
- Verification tools later replay the proof from off-ledger storage and ledger entries.
Inspect Figure 30.3 to separate the small cryptographic job a constrained sensor can own from the ledger duties delegated to a gateway.
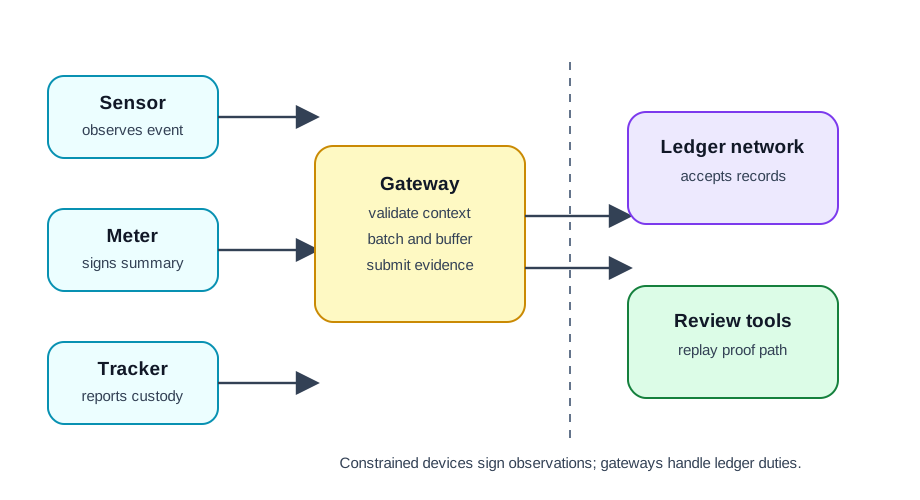
Read Figure 30.3 from the small device to the gateway. The device sees and signs an event with work its chip can bear. The gateway checks local facts, queues data through an outage, groups records, and sends short proof. The ledger peers accept records under shared rules. Later tools replay proof from the off-ledger store and ledger entries. This split keeps peer state, long history, group traffic, and ledger repair away from the sensor. Passing on the work does not hide who made the claim: the signed event must name the device and each change made by the gateway.
30.7 Limitation 3: Latency And Control Fit
This section: Limitation 3: Latency And Control Fit — Ledger acceptance is not a real-time control mechanism.
Ledger acceptance is not a real-time control mechanism. Even a fast permissioned system still adds agreement, ordering, persistence, monitoring, and failure handling. That is useful for evidence. It is not where safety decisions should wait.
Use this rule:
- Immediate safety or control: Keep at device, gateway, or edge service.
- Operational alerting: Keep in telemetry and monitoring paths.
- Shared evidence: Record compact proof or milestone on ledger.
- Settlement or review: Use ledger records after the operational event.
For example, a cold-chain alert should fire through the telemetry path. The ledger can later record the exception summary, handoff context, and proof fingerprint.
Use Figure 30.4 to decide which actions must complete now and which shared records may wait until after the operational event.
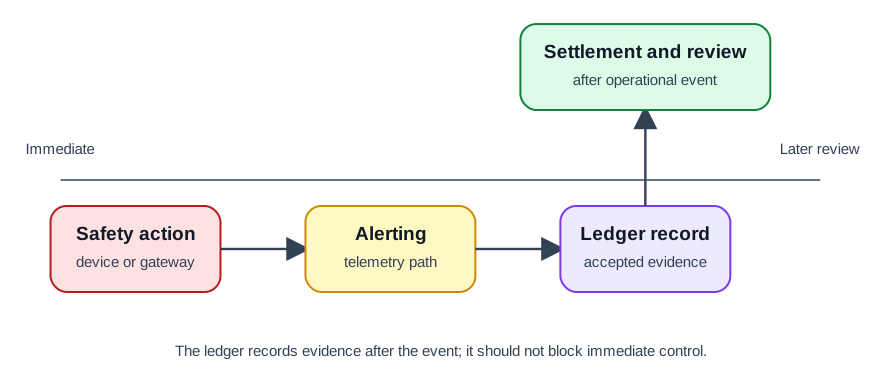
Read Figure 30.4 from immediate work to later review. Safety and control remain at the device, gateway, or edge service because they cannot wait for ledger acceptance. Operational alerts use the telemetry and monitoring path, where staff can see current conditions. Shared evidence, settlement, and review happen after the event through compact ledger records. In the cold-chain example, the telemetry path must fire the alert first; the ledger may later retain an exception summary, handoff context, or proof fingerprint. This timing boundary prevents a durable record mechanism from becoming an unsafe real-time control dependency.
30.8 Limitation 4: Privacy And Correctability
This section: Limitation 4: Privacy And Correctability — Ledger data is deliberately hard to change.
Ledger data is deliberately hard to change. That is useful for shared evidence and risky for data that may be sensitive, wrong, duplicated, or subject to retention limits.
Do not place sensitive raw data directly on a shared ledger. Prefer patterns where the ledger stores:
- A fingerprint of an off-ledger batch.
- A reference to a governed record location.
- A custody or identity event.
- A signed exception summary.
- An agreement outcome derived from accepted evidence.
Keep off ledger:
- Personal data and user identifiers.
- Raw sensor streams.
- Large files and logs.
- Values that may need correction.
- Data that should not be replicated across all participants.
30.9 Limitation 5: Governance And Operations
This section: Limitation 5: Governance And Operations — Many weak blockchain proposals describe the ledger but not the operating model.
Many weak blockchain proposals describe the ledger but not the operating model. A shared ledger is also a shared responsibility system.
Before approval, identify:
- Who can write, read, validate, and review records.
- Who admits new participants and removes old participants.
- Who changes agreement rules.
- Who owns key recovery and suspension.
- What happens during participant outage or gateway outage.
- How duplicate, delayed, or replayed events are handled.
- How disputes are reviewed when the off-ledger record and ledger record disagree.
Before approving the ledger, use Figure 30.5 to check who needs shared proof, who runs each part, and how a later claim can be tested.
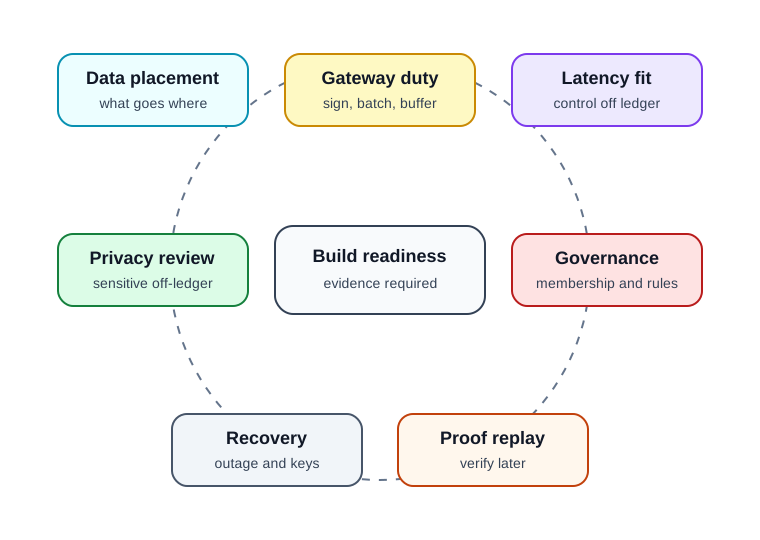
The readiness record in Figure 30.5 starts by naming which parties need a shared fact. Data placement keeps raw telemetry and correctable records off ledger; gateway duties cover signing, batching, buffering, and replay. Latency fit keeps real-time control and alerts outside ledger acceptance, while privacy review checks replicated data. Governance assigns membership, rule changes, key recovery, and suspension. Failure review covers outages, duplicates, delays, and inconsistent records. Finally, proof replay retrieves the raw batch and metadata, recomputes the hash, checks the signature, and compares the ledger and correction record. Approval needs evidence across these areas, not just a running ledger node.
30.10 Worked Example: Meter Ledger Stress Test
This section: Worked Example: Meter Ledger Stress Test — A campus energy-sharing system has several building operators, shared meters, and charging points.
A campus energy-sharing system has several building operators, shared meters, and charging points. The project team proposes writing every meter reading to a ledger so each operator can trust the totals.
30.10.1 Stress Test
Transaction pressure: Raw readings are frequent operational data. Writing every reading to the shared history creates avoidable load and makes later correction difficult.
Resource boundary: Meters should not participate in ledger validation. They should sign readings or send readings over an authenticated channel to a gateway.
Latency fit: Charger control and safety actions cannot wait for ledger acceptance. They remain in the local control path.
Data placement: Raw readings stay in telemetry storage. The ledger records period fingerprints, meter identity actions, exception summaries, and accepted settlement outcomes.
Privacy and correction: User-level charging detail should not be replicated across all participants. Shared records should be aggregated and bounded to the verification need.
Governance: Operators need explicit rules for participant membership, meter replacement, gateway outage, delayed submission, and proof replay.
30.10.2 Recommendation
Use off-ledger telemetry storage with signed meter records. Write only compact period fingerprints, meter identity changes, exception summaries, and accepted settlement outcomes to the shared ledger. Reject direct raw telemetry on ledger and reject real-time control through ledger acceptance.
30.11 Implementation Readiness Checklist
This section: Implementation Readiness Checklist
Use this checklist before approving a blockchain implementation:
- Fit statement: The design names the parties that need shared evidence.
- Data placement: Raw telemetry, logs, and files are separated from ledger evidence.
- Gateway duty: The gateway signing, batching, buffering, and replay behavior is specified.
- Latency boundary: Real-time control and alerting do not depend on ledger acceptance.
- Privacy review: Sensitive or correctable data is kept off ledger.
- Governance model: Membership, rule changes, key recovery, and participant suspension are assigned.
- Failure behavior: Outage, duplicate, delayed, replayed, and inconsistent records have review paths.
- Proof replay: A reviewer can recompute a fingerprint from off-ledger records and compare it with the ledger record.
30.12 Approve Boundaries, Not Ledgers
This section: Approve Boundaries, Not Ledgers — The safest IoT blockchain decision starts by drawing a boundary.
The safest IoT blockchain decision starts by drawing a boundary. The ledger should carry the small facts that several parties must verify later. The telemetry store, alert path, gateway buffer, and control loop should keep doing the fast operational work.
Think of the ledger as the signed receipt drawer, not the factory floor. A receipt can prove that a handoff, batch fingerprint, meter period, or exception was accepted. It should not become the place where every raw reading waits, every safety action is decided, or every device tries to maintain shared history.
For a campus energy system, that boundary might put MQTT ingestion, a stream processor, a time-series database, charger-control rules, and operator dashboards outside the ledger. The ledger receives a signed 15-minute period summary, a SHA-256 fingerprint for the off-ledger batch, the gateway signer, the time window, and the settlement state. If the ledger is slow or unavailable, chargers still follow local safety policy and telemetry still lands in storage; the gateway marks the later submission as delayed instead of pretending consensus was part of the live control path.
That boundary also protects correction and privacy workflows. A wrong meter calibration, missing packet, or privacy redaction can be handled in operational storage with a visible correction record. The ledger should preserve the accepted proof trail, not replicate every personal charging event or make every corrected reading permanent across all participants. Approve the design only when the team can name what is on ledger, what stays off ledger, and how a reviewer reconstructs the proof.
If any stakeholder cannot explain the boundary in one diagram, pause the implementation. The missing diagram usually means the ledger is carrying jobs that belong to telemetry, control, privacy review, or governance.
30.13 Ledger Readiness Record
This section: Ledger Readiness Record — A readiness record turns a blockchain proposal into a checkable architecture decision.
A readiness record turns a blockchain proposal into a checkable architecture decision. It should be short enough to review in a design meeting and specific enough to reject vague promises.
| Record Field | What To Write | Reject If Missing |
|---|---|---|
| Shared fact | The handoff, fingerprint, identity action, exception, or settlement result that multiple parties need to trust. | The proposal says "all sensor data" or "the whole dashboard." |
| Off-ledger source | Where the raw batch, timestamp source, signer, hash method, and retrieval rule live. | The fingerprint is stored but the original batch cannot be replayed. |
| Gateway duty | Who signs, batches, buffers, retries, and marks delayed submissions during outage. | Constrained devices are expected to behave like full ledger nodes. |
| Control boundary | Which alerts and safety actions stay local even when the ledger is slow or unavailable. | Control waits for consensus before acting. |
| Governance owner | Who admits participants, suspends keys, changes rules, handles disputes, and approves recovery. | The network is described, but operating authority is not assigned. |
For the campus energy example, a useful readiness record names the gateway service as the ledger writer, the gateway certificate or key material used for signatures, the timestamp source, the canonical serialization used before hashing, and the off-ledger store that keeps the raw batch. It also names the batch identifier, period boundary, reading count, hash algorithm, idempotency key, and outage marker so a duplicate retry or delayed submission does not look like a fresh settlement event.
The same record needs operating ownership. Write who can add a building operator, rotate a gateway certificate, revoke a compromised writer, change the settlement rule, and approve a correction when raw telemetry and a ledger fingerprint no longer match. A prototype that can write one transaction is not enough; the production design has to survive key loss, gateway outage, participant suspension, batch replay, and disputed readings without inventing rules during the incident.
A reviewer should be able to test the record by replaying one sample day. Retrieve the off-ledger batch, sort it with the recorded rule, recompute the hash, verify the gateway signature, compare the result with the ledger transaction, and inspect any correction record. If that replay cannot be performed from the documented artifacts, the ledger adds permanence without adding trustworthy evidence.
30.14 Load and Replay Break Designs
This section: Load and Replay Break Designs — The load problem appears before the cryptography does.
The load problem appears before the cryptography does. Ten thousand devices reporting once per minute produce about 167 readings per second. The same fleet reporting every five seconds produces 2,000 readings per second. If each reading becomes a shared ledger transaction, the architecture has moved an operational telemetry problem into the most expensive path.
Batch anchoring changes the shape of the problem. A gateway can collect many readings, write them to operational storage, compute a hash over the accepted batch, and submit one compact record for the period. Later, an auditor retrieves the batch, recomputes the hash with the recorded method, and compares it with the ledger entry. The ledger proves that the accepted batch has not silently changed; the telemetry store still handles query, correction, retention, and alerting.
The internal ledger work is still real work. In a permissioned deployment, peers or validators must authenticate writers, order accepted transactions, validate rules, persist state, expose monitoring, and recover after outages. Those duties may be reasonable for period summaries and custody events, but they are wasteful for raw readings that a telemetry database can ingest, index, compress, expire, and correct more directly. Pushing every reading through consensus also makes the privacy blast radius wider because more participants receive data that should have stayed behind an access-controlled operational boundary.
A robust gateway design uses backpressure and durable queues before the ledger client. The queue keeps the batch id, time window, reading count, previous-batch pointer when needed, canonical sort rule, hash algorithm, signer, and retry state. Ledger submission then becomes an idempotent milestone for a bounded period, not a per-packet dependency. During outage recovery, the gateway submits late evidence with an explicit outage marker so reviewers can distinguish delayed proof from live telemetry.
That proof only works when replay metadata is preserved. The record needs the batch id, hash algorithm, canonical ordering rule, timestamp source, signer identity, ledger transaction id, and a policy for missing or corrected readings. Without those fields, the ledger stores a fingerprint that no one can reliably recheck.
Common Failure Patterns
This section: Common Failure Patterns
This creates unnecessary load and makes operational data hard to query, correct, retain, or remove. Anchor compact evidence instead.
Control actions need predictable local response. Use the ledger for later evidence, not for immediate safety behavior.
The ledger network needs rules for membership, write authority, rule changes, outages, and recovery. Without those rules, the shared history becomes an operating liability.
A fingerprint is useful only if the off-ledger batch, method, timestamp source, signer, and review process are also preserved.
30.15 Knowledge Check
This section: Knowledge Check
30.16 Knowledge Check
This section: Knowledge Check
30.17 Match Limits To Design Responses
This section: Match Limits To Design Responses
30.18 Sequence Readiness Checks
This section: Sequence Readiness Checks
30.19 Summary
This section: Summary — Blockchain limitations for IoT are practical design constraints.
Blockchain limitations for IoT are practical design constraints. High event volume, constrained devices, latency-sensitive control, sensitive data, governance, and recovery all need explicit handling. A strong implementation writes compact shared records to the ledger, keeps raw telemetry and control off ledger, uses gateways at the resource boundary, and proves that later verification can replay the proof path. If the design cannot show those records, it is not ready for implementation.
30.20 Key Takeaway
This section: Key Takeaway — Blockchain limitations are design constraints: latency, throughput, privacy, key custody, governance, and recovery often matter more than ledger novelty.
Blockchain limitations are design constraints: latency, throughput, privacy, key custody, governance, and recovery often matter more than ledger novelty.
30.21 What’s Next
This section: What’s Next
- Use Blockchain Lab to practice tracing signed events and proof replay.
- Use Smart Contracts and Architectural Patterns when agreement logic and gateway patterns are the next design question.
- Revisit Blockchain Fundamentals for IoT for the ledger concepts behind these limits.
Find help
3 reviewed answers.
Where should I start in a module?
Open the module page from the sidebar to see its chapters in order. Use the module map to return to a topic you need.
Modules and pathsReviewed
What can I try when a project does not work?
Check the symptom, then work through the diagnostic steps. Keep the error message and the smallest example that reproduces it.
When you are stuckReviewed
How do interactive examples work?
Use the interactive guide to check how examples and simulations work before changing your project.
Interactive examples guideReviewed