11 IoT Enablers: Compute and Readiness
More
Depth: Practitioner
Progress saves as you read. Mark sections complete as you go; your progress appears in the sidebar.
11.1 Start With the Decision
This section: Start With the Decision — A platform feature is not an enabler if the team cannot operate it.
A platform feature is not an enabler if the team cannot operate it. Compute, tools, skills, and rollout limits must be checked together.
11.2 Route Overview
This section: Route Overview — This is part 1 of 2.
This is part 1 of 2. Continue with IoT Enablers: Records and Convergence.
11.3 Part Objectives
This section: Part Objectives
- Assess compute and development enablers for an IoT release.
- Review coupling, ownership, and rollout constraints.
11.4 Chapter Roadmap
This section: Chapter Roadmap
- Start With the Release Constraint
- Overview: Enablers Are Evidence Gates
- Computing and Development Enablers
- The architectural transition in one sentence
- Review Couplings Before Rollout
11.5 Start With the Release Constraint
This section: Start With the Release Constraint — Picture a farm sensor that works on a bench but fails after one wet night.
Picture a farm sensor that works on a bench but fails after one wet night. Buying a faster chip will not fix a bad case or a weak service plan. Start with the release block, then choose the capability that removes it.
An enabler is a capability that lets the whole design work in its real setting. A protocol is an agreed set of rules for how devices exchange data. A gateway is a device or service that joins one system boundary to another. A named part proves only that the part exists. A bench test proves only a narrow case. Release needs evidence that sensing, power, links, data, safety, security, updates, and human work fit together.
Ask one gate at a time:
- What blocks release now?
- Is the physical event sensed well?
- Can the device last between service visits?
- Can data cross the real site?
- Can a local action stay safe?
- Is the record fit for the decision?
- Can identity and access be managed?
- Can the fleet change without guesswork?
- Can people act on the result?
- Which proof closes the gate?
One enabler can weaken another. More radio use can drain power. More local work can raise heat and support cost. Practitioner reviews those links before rollout. Under the Hood builds the readiness record and tests coupled limits. Those details may reopen a green gate. They never make a part name proof of system readiness.
Retell the gate. A real need sets the job. A field limit blocks release. One capability may help. The team tests that capability. It checks linked costs. A named owner accepts the result. The next change can reopen it.
Architectural enablers are easiest to understand when a release constraint blocks progress. The design may need more local compute, a better communication path, a safer interface, lower energy use, clearer tooling, or a production review before it can leave the prototype stage.
Start with that constraint. An enabler is not a feature decoration; it is the capability that makes the chosen architecture deployable, supportable, and testable under real operating conditions.
11.6 Overview: Enablers Are Evidence Gates
This section: Overview: Enablers Are Evidence Gates — Architectural enablers are the conditions that make an IoT system practical, supportable, and worth operating.
Architectural enablers are the conditions that make an IoT system practical, supportable, and worth operating. They include sensing, local computing, physical integration, energy behavior, communication, data quality, security, device management, and adoption workflow.
A design is not ready because it names a chip, radio, protocol, gateway, or cloud platform. It is ready when each enabler has evidence and the enablers work together as a managed physical-system feedback loop.
That distinction is practical: a named component answers what could be bought, while enabler evidence answers whether the installed system can detect the event, survive site conditions, produce trustworthy records, and give people a clear action path.
Inspect Figure 11.1 before judging overview: enablers are evidence gates; it depicts: Use enablers as a readiness gate before treating a component choice as a deployable architecture. Focus first on Physical Purpose, then on sleep, wake, maintain.
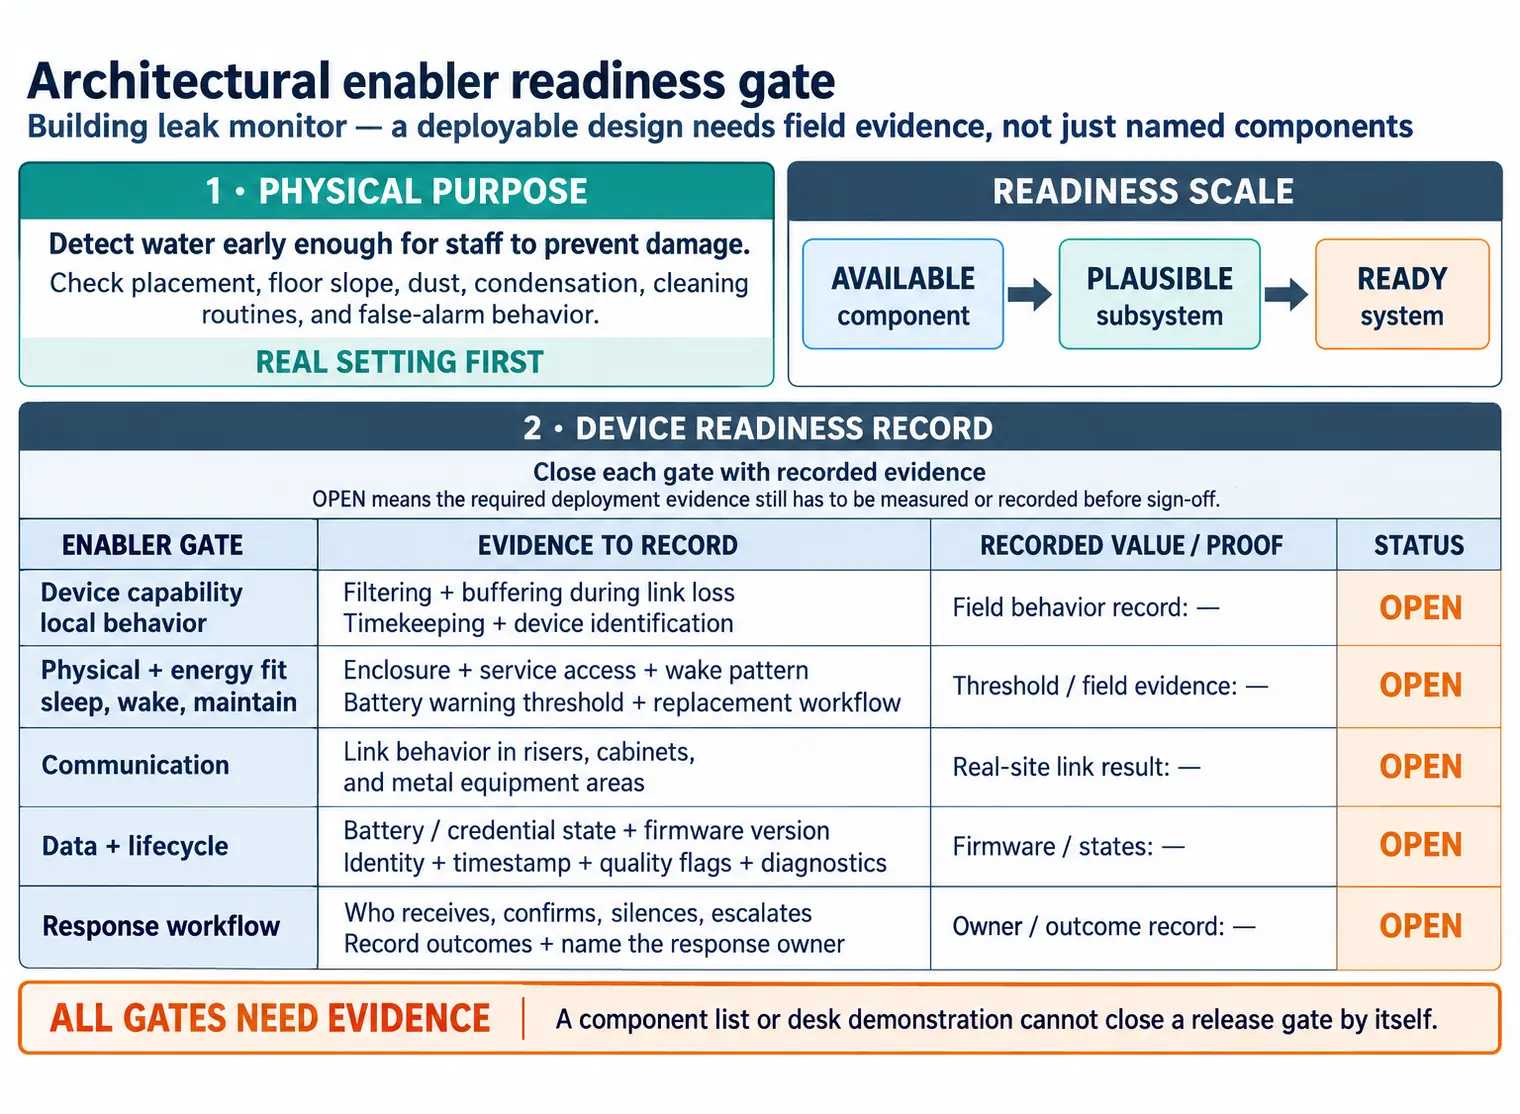
The readiness gate in Figure 11.1 runs from Physical Purpose to sleep, wake, and maintenance, with evidence required at every gate.
Component Exists
A part, protocol, library, profile, or service can be used. This is useful inventory, but it is not system readiness.
Subsystem Works
A prototype shows one part of the system working under controlled conditions. The result still needs site, lifecycle, and support evidence.
System Has Evidence
The installed design has evidence across physical sensing, power, communication, data quality, security, lifecycle, and workflow.
For overview: enablers are evidence gates, inspect Figure 11.2 at Supportable. Its visible premise is: The foundation set exposes the responsibilities a deployed IoT system must carry. Then compare sleep, wake, maintain.
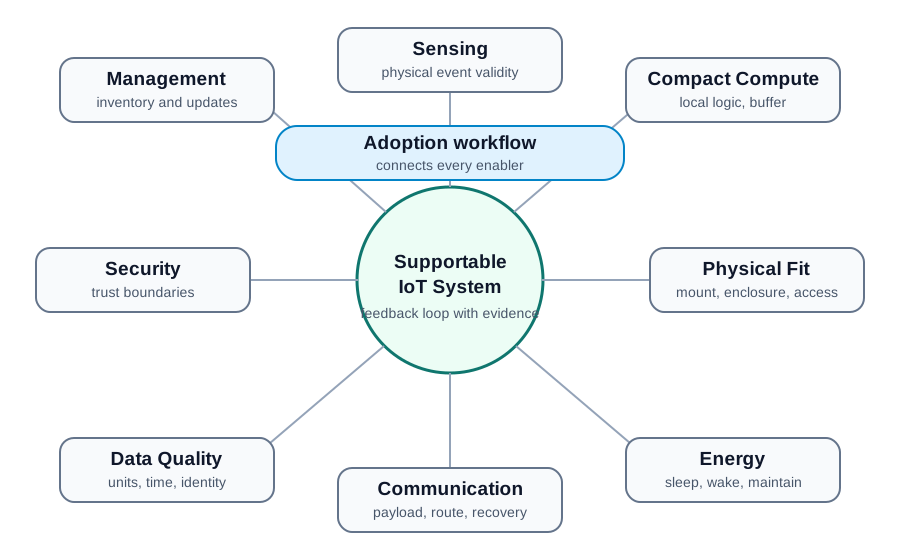
The water-leak path in Figure 11.2 starts with a sensing circuit that qualifies water presence. Firmware timestamps and debounces the event, and the radio sends a compact authenticated message. A gateway applies the data contract; the platform links it to an asset before an alarm reaches a named facilities owner. The surrounding bands show work that spans the path: enclosure and power fit, units and missing-data flags, credential and update management, and support workflow. A named sensor or radio only proves that part exists. To call the alarm supportable, check the handoffs, sleep and wake behavior, and the person who must act on it.
This map identifies what the system must provide. The Practitioner placement map later identifies where those responsibilities execute and who owns the interfaces between them.
The Foundation Set
Sensing and Actuation
Define the physical event, validity limits, calibration state, false positives, false negatives, and safe behavior when a sensor or actuator fails.
Compact Computing
Check local filtering, thresholds, buffering, timekeeping, offline behavior, firmware constraints, and safe defaults near the physical event.
Physical and Energy Fit
Review enclosure, mounting, antenna position, service access, sleep states, transmit windows, charging, replacement, and outage behavior together.
Communication and Data
Match payload timing, coverage, capacity, retries, topology, identity, units, timestamps, missing-data handling, and quality flags to the decision.
Security and Management
Control identity, credentials, authorization, updates, logs, diagnostics, provisioning, monitoring, rollback, replacement, and retirement.
Adoption Workflow
Name installers, operators, support owners, escalation paths, override rules, training needs, and outcome review before the system is approved.
11.7 Computing and Development Enablers
This section: Computing and Development Enablers — It is tempting to explain IoT’s growth as “processors kept getting faster.” That is only half the story, and it stops being a useful model around the mid-2000s.
It is tempting to explain IoT’s growth as “processors kept getting faster.” That is only half the story, and it stops being a useful model around the mid-2000s. Earlier CMOS generations benefited from Dennard scaling: as transistors shrank, voltage and capacitance also fell, so designers could raise clock frequency without making power density grow without bound. A useful first-order switching-power model is
where is the fraction of gates switching, is switched capacitance, is supply voltage, and is clock frequency. The square on matters. When voltage scaling slowed, raising pushed power and heat upward even though transistors were still becoming smaller. Leakage power also became a larger share of the budget. Around 2005, commercial processor clock growth consequently flattened: the thermal envelope, rather than transistor availability alone, became the hard boundary.
The response was architectural. Extra transistors were spent on multiple cores, larger caches, vector units, accelerators, radios, and power-management domains instead of indefinitely faster single-thread execution. If a workload has parallel fraction and runs on cores, Amdahl’s law gives the upper bound
For on four cores, , not . The serial part, coordination overhead, memory bandwidth, and energy budget remain. Moore-style transistor-count growth can provide more possible machinery, but it does not guarantee proportional application speed, and economics and fabrication limits bound how long density growth can continue.
For IoT, the consequence is more useful than the history: capability comes from a distributed stack of specialised resources. A tiny always-on core can qualify an event; a radio accelerator can move a short authenticated frame; an edge gateway can batch or infer; a cloud service can aggregate across a fleet. The design question is therefore “where should this work execute under the latency, energy, trust, and lifecycle constraints?” rather than “which single processor is fastest?”
| Enabler layer | What changed | What it enables | Evidence to demand |
|---|---|---|---|
| Miniaturised sensing and compute | More functions fit in smaller, cheaper packages | sensing and local decisions near the physical event | accuracy, thermal behavior, interface ownership, and enclosure proof |
| Batteries and power management | lower sleep current, retained state, power islands | untethered and intermittently active devices | measured state durations, wake cost, lifetime calculation, and replacement plan |
| Communications | low-power radios, wired field buses, IP gateways | device-to-edge-to-platform paths | coverage, airtime, retry, congestion, and outage behavior |
| Development resources | accessible languages, SDKs, APIs, and modular runtimes | faster implementation and integration | version pinning, footprint, security maintenance, and reproducible builds |
| Data contracts | language-neutral formats and schemas | independently developed components can exchange meaning | units, timestamps, identifiers, compatibility, and invalid-data rules |
| Platforms and visualisation | registries, brokers, storage, analytics, dashboards | fleet operations and human decisions | ownership, authorization, retention, alert routing, and receiver outcomes |
Walk the stack in order for a battery leak sensor. The sensing circuit first turns water presence into a qualified local event. Firmware timestamps and debounces it rather than streaming raw samples. The radio sends a compact, authenticated message. A gateway or broker applies the data contract. The platform associates it with a registered asset, and the visualisation routes an alarm to a named facilities owner. Removing any one link—battery-life proof, a stable schema, authenticated communication, or an owned alert—turns impressive component capability into an incomplete system.
The end of scaling is best read as two coupled histories rather than one transistor-count curve. Figure 11.3 shows power density and clock growth flattening while integration and core count continue.

At the dashed voltage and frequency wall in Figure 11.3, the clock-frequency track stops rising even though transistor count continues. Power density also flattens, so simply driving one core faster is no longer the general route to more work. Core count rises instead, followed by specialised accelerators and integrated radios. The lower IoT panel carries that change into system architecture: processing is divided across device, edge, and cloud. Software must therefore expose parallel work and place it where latency, energy, data, and ownership boundaries permit.
The end of voltage-and-frequency scaling did not end progress; it changed progress from “one core runs the same program ever faster” to “heterogeneous local, edge, and cloud resources cooperate under explicit power, data, and management contracts.”
11.8 Review Couplings Before Rollout
This section: Review Couplings Before Rollout — Enablers are not independent checklist items.
Enablers are not independent checklist items. Most IoT failures appear where dimensions meet: a smaller enclosure blocks the antenna, a stronger security boundary changes provisioning, a longer sleep interval changes data freshness, or a dashboard creates alerts no one owns.
A practitioner should review the interfaces between enablers before approving a pilot or release candidate.
11.8.1 Place Responsibilities Before Testing Couplings
The foundation set names the capabilities a supportable system needs, but it does not decide where those capabilities execute. Map the field device, any gateway or edge tier, the platform service, and the human workflow before reviewing their couplings; every handoff needs an accountable owner, a fallback, and evidence for both normal and degraded operation.
A typical software stack gives each of those three tiers a recognizable shape. A constrained field device usually carries a hardware abstraction layer, an RTOS or bare-metal scheduler, and a communication block split into field protocols and IoT protocols, with a remote-management path threaded through all three. A gateway or edge tier adds a general-purpose OS or RTOS, an application runtime that can host updatable code, network management, and a data-management-and-messaging layer that queues telemetry during an outage and forwards it in a consistent shape once the platform is reachable. The platform service itself is usually organized around connectivity and message routing at the base, an OS or PaaS underneath, and a set of named responsibilities above it: device registry, device management, data management, event management and analytics, and application enablement for dashboards, reports, and API access. Security, common data ontologies, and developer tools and SDKs cut across all three tiers rather than belonging to any one of them. Naming which of those specific blocks a given design provides -- and which it is missing -- is a more testable placement sentence than "the gateway handles local processing."
Inspect @embed-fig-enablers-fundamentals-responsibility-placement to ask where each field, edge, platform, and human duty runs, who owns its handoff, and what fallback proves it can fail safely.

Read the map from the field device through the edge and platform to the person who acts. For each key job, write where it runs and who owns the next handoff. Then follow the return path for settings, keys, commands, and updates. A failed link must have a named fallback and a fact that proves the fallback worked. The four rails show that field fit, data rules, trust, and support cross more than one tier. Once those duties are placed, use the loop below to find which nearby parts need a new test when a site, link, or owner changes.
At place responsibilities before testing couplings, Enabler Coupling Loop makes the architecture testable. In Figure 11.4, Data frames this claim: Design changes should trigger focused checks on adjacent enablers, not isolated sign-off. Read it against Enabler Coupling Loop.
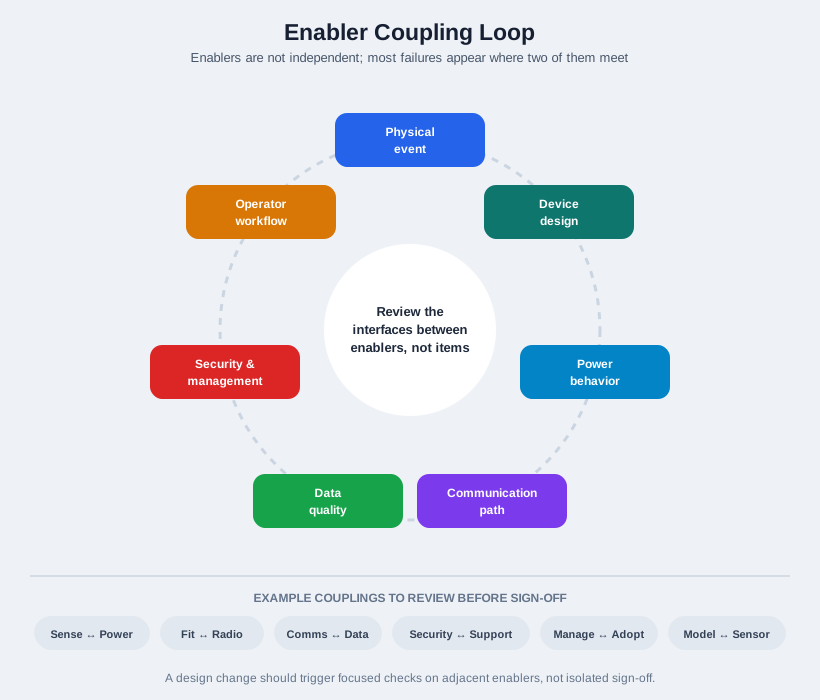
The ring in Figure 11.4 shows why one design change needs more than one sign-off. A new sensing interval can alter wake time and battery service; a new enclosure can change antenna fit and field access. Communication changes can lose timing or quality fields that the data pipeline needs. Security and support must meet at credential recovery, while a changed model may require new sensor evidence. The point of the loop is to test adjacent responsibilities after a change, not to declare every component ready in isolation. Name the affected pair, the evidence to repeat, and the owner before accepting the new design.
Coupling Questions
Scenario: Building Leak Monitoring
A facilities team wants to monitor water leaks in mechanical rooms, risers, and equipment areas. The architecture should not be approved merely because a leak sensor, gateway, and dashboard can be demonstrated on a desk.
Physical Event
Detect water early enough for staff to prevent damage. Check sensor placement, floor slope, dust, condensation, cleaning routines, and false alarm behavior.
Local Behavior
Decide what is filtered locally, what is buffered during link loss, how time is maintained, and how staff identify the device after installation.
Power and Coverage
Record wake pattern, alarm behavior, battery warning threshold, replacement workflow, and link behavior in risers, cabinets, and metal equipment areas.
Data and Lifecycle
Store device identity, location, zone, timestamp, alarm state, battery state, quality flags, credential state, firmware version, and diagnostic access.
Response Workflow
Assign who receives alerts, how they confirm a leak, when they silence an alert, how escalation works, and how outcomes are recorded.
Do not approve an IoT design by listing components. Approve it by showing that every enabler has evidence and that changes in one enabler have been checked against the others.
The practical risk in place responsibilities before testing couplings needs a diagram. Figure 11.5 summarizes it: A compact record makes field evidence, ownership, risks, and review triggers visible. Look at Enabler Readiness Record beside Data and lifecycle.
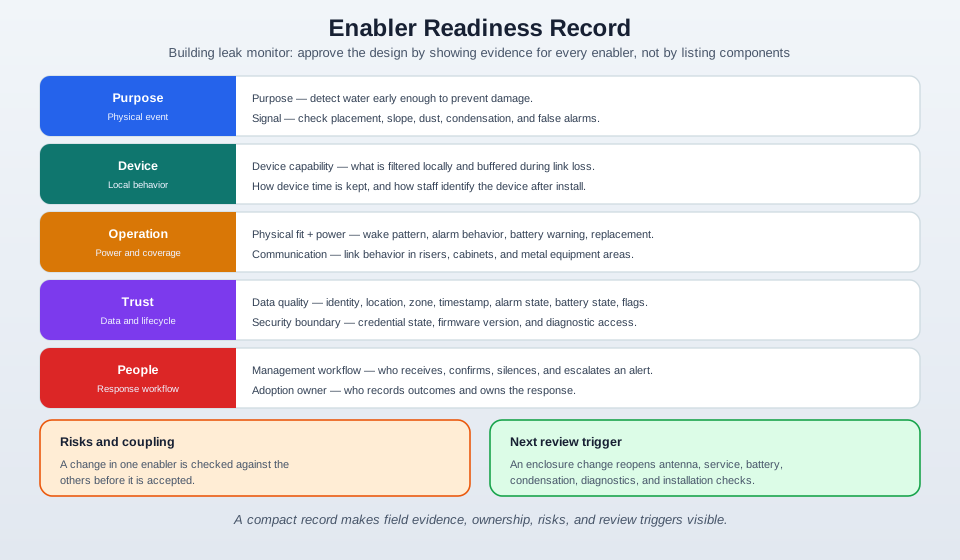
The building leak record in Figure 11.5 follows one event from water presence to an owned response. The local device qualifies and timestamps it, buffers through link loss, and sends an authenticated message to a gateway. The platform maps the message to an asset and alerts facilities, which must confirm, silence, or escalate the event. The lower fields keep placement, condensation, alarm behavior, battery replacement, data quality, credentials, and diagnostics with the release decision. An enclosure change is the review trigger shown in the figure; it reopens antenna, service access, power, and installation checks. The record makes that coupling visible to the next reviewer.
11.9 Continue to the Next Part
This section: Continue to the Next Part — Carry this evidence into IoT Enablers: Records and Convergence, which begins with Records Make Readiness Auditable.
Carry this evidence into IoT Enablers: Records and Convergence, which begins with Records Make Readiness Auditable.
Find help
3 reviewed answers.
Where should I start in a module?
Open the module page from the sidebar to see its chapters in order. Use the module map to return to a topic you need.
Modules and pathsReviewed
What can I try when a project does not work?
Check the symptom, then work through the diagnostic steps. Keep the error message and the smallest example that reproduces it.
When you are stuckReviewed
How do interactive examples work?
Use the interactive guide to check how examples and simulations work before changing your project.
Interactive examples guideReviewed