10 Network Design: Tail Risk and Scope
More
Depth: Practitioner
Progress saves as you read. Mark sections complete as you go; your progress appears in the sidebar.
10.1 Start With the Decision
This section: Start With the Decision — A network that meets its average target may still fail its worst users.
A network that meets its average target may still fail its worst users. Scope and tail risk must be clear before an architecture is chosen.
10.2 Route Overview
This section: Route Overview — This is part 1 of 2.
This is part 1 of 2. Continue with Network Design: Evidence and Architecture Workflow.
10.3 Part Objectives
This section: Part Objectives
- Define network scope, service targets, and tail risk.
- Separate design assumptions from measured evidence.
10.4 Chapter Roadmap
This section: Chapter Roadmap
- Start With One Message That Must Arrive
- In 60 Seconds
- Phoebe’s Field Notes: Why “Mobility” Sits Next to “Walls, Metal, Water” on the Site-Constraint List
- Prerequisites
- Start With Communication Promise
- Match Protocols to Site Risk
- Validate Tail, Not Average
- What This Chapter Does
10.5 Start With One Message That Must Arrive
This section: Start With One Message That Must Arrive — A gateway is the local point that joins device links to another network.
A gateway is the local point that joins device links to another network. Latency is the time a message takes to arrive. A payload is the useful data in that message. A protocol is the shared set of rules used to send it.
Picture a freezer alarm that must reach a night guard. Write the promise first: what is sent, how soon it must arrive, who receives it, and what happens after a miss. Then draw the path and choose parts that can meet that promise.
Test the busy and broken cases. A short path may have a weak link. A strong radio may waste battery. A fast plan may fail when many alarms start together or when the local link to the wider network is lost.
This one-message story cannot choose a full design. It does not prove coverage, power, safety, or service care. Models can answer some questions, but only bench and field work can settle physical claims.
Use the Practitioner sections to build the network evidence route. Use Under the Hood for traffic, link, model, and test limits. The deeper chapters add detail to the promise; they do not replace it.
Walk the freezer alarm once. Name the sensor. Name the room. Name the guard. Name the action. Set the send rate. Set the alarm time. Set the safe delay. Set the miss rule. Mark every link. Mark every power source. Mark every owner. Draw the return path too.
Now count traffic. Count normal reports. Count alarm bursts. Count replies. Count retries. Count new joins. Count service checks. Count a large update. Put each in its busy window. Keep spare room. Put urgent work first. Move bulk work away from alarms.
Check the site. Walk the path. Mark walls. Mark metal. Mark floors. Mark wet rooms. Mark hot rooms. Mark moving parts. Mark weak power. Mark service access. A neat map is only a first guess.
Test one link at a time. Send near. Send far. Add other traffic. Cut power. Restart the node. Restart the local bridge. Cut the wider link. Fill the local queue. Restore the path. Check order. Check old messages. Check the guard saw one true alarm.
Compare choices with the same facts. A star is simple but needs its centre. A mesh may reach around loss but adds relay work. A wired path may be stable but hard to fit. A mobile service may reach far but adds an outside owner. Record each gain and cost.
Use a model for a named doubt. Ask about range. Ask about load. Ask about delay. State each guess. Vary it. Find the weak point. Then test that point in the field. Do not let a smooth chart hide a rough site.
Close the first record. Keep the promise. Keep the path. Keep the busy case. Keep the failed case. Keep the measured result. Keep the open risk. Name the next test. Name the decision owner. Review it when the site or traffic changes.
Picture a freezer alarm, occupancy reading, or machine-status update leaving a device and needing to reach the right place at the right time. Network design starts by naming that communication promise: payload, interval, receiver, path, delay tolerance, failure behavior, and evidence. Only then can topology, gateway placement, protocol choice, and validation make sense.
10.6 Learning Objectives
This section: Learning Objectives
By the end of this chapter, you will be able to:
- Explain why IoT network design follows an evidence route rather than a single topology drawing.
- Identify the questions that must be answered before choosing a protocol, topology, gateway plan, or simulator.
- Distinguish paper design, simulation, packet capture, field pilot, and operations evidence.
- Recognize when a network claim is too vague to support deployment.
- Navigate the network-design chapter sequence without confusing introductory concepts with detailed tool or methodology work.

10.7 Prerequisites
This section: Prerequisites
This introduction assumes you can read basic network diagrams and have seen:
- Networking basics: packets, addressing, routing, and layers.
- IoT protocol families: short-range, mesh, LPWAN, Wi-Fi, and cellular options.
- IoT reference models: edge, gateway, fog, and cloud roles.
10.8 Start With Communication Promise
This section: Start With Communication Promise — Network design begins by naming what communication must reliably happen, not by choosing a fashionable topology.
Network design begins by naming what communication must reliably happen, not by choosing a fashionable topology. A freezer alarm, a soil sensor, a smart-lighting command, and a factory vibration stream all need different latency, power, reliability, ownership, and recovery behavior. A design review that starts with “mesh is reliable” or “LoRaWAN has long range” skips the question that matters: what promise is the network making to the application, the operator, and the person affected by failure?
The first design task is to turn the deployment story into a communication promise: which device sends what payload, how often, to which receiver, through which gateway or backhaul, and what should happen when the path is delayed, duplicated, blocked, or unavailable. A warehouse freezer alarm might promise that an exception reaches the dashboard and duty phone within two minutes even during shift change. A campus air-quality node might promise that fifteen-minute readings are eventually delivered, flagged when stale, and locally buffered during a Wi-Fi outage. Those two promises can both be “IoT telemetry,” but they lead to different protocol, power, storage, alerting, and support choices.
Inspect Figure 10.1 and ask what evidence would prove the network’s communication promise under the difficult operating case.
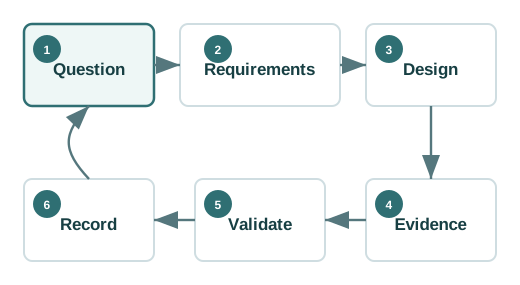
Read Figure 10.1 from the service promise to a test. The freezer case turns the need into delivery within two minutes during shift change. That claim can fail or pass. Next compare the proposed topology, radio, gateway, and zones with targets for delivery, delay, join, and recovery. Give each claim the right proof: a paper sum, RF survey, packet trace, model, pilot log, or work metric. The review takes those results back to the first promise. The design record keeps assumptions, limits, and open risks. Hard-case proof, not a protocol name or mean result, must support the network.
The route in the figure keeps early design conversations honest. Requirements translate the promise into measurable targets such as delivery ratio, latency percentile, join success, battery interval, recovery time, or maximum unsupported outage. Candidate designs then compare topology, radio, IP addressing, broker, gateway, and segmentation choices against those targets. Evidence planning decides which claims need a paper calculation, site walk, RF survey, packet capture, simulation, pilot log, or operations metric. Validation connects that evidence back to the original promise before the team records a design basis.
- Traffic: Separate periodic telemetry, event alarms, commands, joins, time sync, firmware updates, diagnostics, and maintenance traffic before estimating load.
- Topology: Compare star, mesh, tree, star-of-stars, gateway-mediated, and hybrid designs against the actual site, traffic, power, and ownership constraints.
- Operation: Name who provisions, monitors, updates, troubleshoots, replaces, and retires each network segment, because an unowned network is not deployable.
10.9 Match Protocols to Site Risk
This section: Match Protocols to Site Risk — Different IoT networks fail in different ways, so the practitioner layer is about matching evidence to the failure mode instead of collecting generic artifacts.
Different IoT networks fail in different ways, so the practitioner layer is about matching evidence to the failure mode instead of collecting generic artifacts. LoRaWAN star-of-stars designs depend on gateway placement, link budget, spreading factor, duty cycle, Adaptive Data Rate behavior, join capacity, duplicate reception, and gateway backhaul reliability. Zigbee, Thread, BLE Mesh, and RPL/6LoWPAN designs depend on powered-router density, parent choice, route repair, sleepy-node polling, multicast behavior, and interference from Wi-Fi or industrial equipment. Wi-Fi, Ethernet, LTE-M, NB-IoT, and private cellular shift risk toward credentials, roaming, subscriptions, NAT and firewall rules, DHCP/DNS availability, SIM lifecycle, AP/controller configuration, and service ownership.
Evidence should match the risk. RSSI/SNR logs and spreading-factor distributions help explain weak LPWAN links, but they do not prove application queueing or alarm handling. Packet captures help explain MQTT publish/ack timing, CoAP retransmissions, TCP reconnects, TLS handshake cost, DHCP lease recovery, or DNS lookup delay, but they do not show future seasonal coverage. RF surveys help with placement and interference, but they cannot prove firmware sleep-state behavior. Gateway and broker metrics reveal joins, retries, queue depth, retained messages, backhaul outages, and authentication failures. Pilot logs show whether installation, maintenance, ownership, and support workflows can keep the network healthy after the first demonstration.
A practical review usually combines a small number of well-chosen evidence sources. For a warehouse alarm system, ask for a floor plan, freezer-row RSSI/SNR samples, gateway placement assumptions, alarm latency percentiles, join behavior after a power event, and battery-current traces during retry bursts. For a smart-building control pilot, ask for powered-router density, route repair time after a router outage, command acknowledgement timing, commissioning ownership, certificate or key rotation process, and local fallback behavior if the cloud path is unavailable. For an outdoor meter network, ask who owns the carrier contract, what happens when coverage changes, and how stale readings are marked for billing or operations.
- List the traffic classes. Include size, interval, burst pattern, priority, retry rule, acknowledgement rule, and acceptable loss or delay.
- List the site constraints. Include walls, metal, water, terrain, floors, mobility, weather, power, gateway access, maintenance windows, and support boundaries.
- List the proof method. Decide what will be shown by paper design, simulation, RF survey, packet capture, pilot logs, operations metrics, or explicit risk acceptance.
10.10 Validate Tail, Not Average
This section: Validate Tail, Not Average — IoT networks often look acceptable in averages while failing at the edge.
IoT networks often look acceptable in averages while failing at the edge. Mean latency can hide delayed alarms. Average packet delivery can hide one basement, freezer room, pump house, or loading bay. Average gateway load can hide a join storm after a power outage. Average current can hide retry bursts that shorten battery life. A simulation with an attractive topology can miss an overloaded gateway queue, a certificate expiry path, a firmware update burst, or a sleepy-node polling delay unless the model includes those mechanisms and the team checks them against field evidence.
Use metrics that expose the risk: delivery ratio by location, latency percentiles, retry distribution, queue depth, route repair time, gateway failover time, backhaul outage duration, battery current by firmware state, join success rate, DNS and DHCP recovery time, TLS handshake duration, broker authorization failures, and command acknowledgement timing. Then connect each metric to an action. A poor SNR distribution might move a LoRaWAN gateway or change ADR policy. Slow route repair might add powered Thread routers or split a Zigbee network. Long MQTT reconnects might change keepalive, session expiry, broker placement, or local buffering. A high current tail might change sampling rate, retransmission limits, firmware sleep states, or the battery-maintenance promise.
The under-the-hood record should also state the model limits. If a tool such as ns-3, OMNeT++, Cooja, TOSSIM, Wireshark, tcpdump, a gateway console, or a cloud IoT platform dashboard contributed evidence, record what it could and could not observe. If a simulation uses ideal propagation, fixed node positions, independent packet loss, or simplified MAC behavior, say which pilot measurement would invalidate it. If a packet capture was taken near one gateway, say which locations and failure modes remain untested. This prevents a design basis from overstating certainty.
- Failure scenarios: Test gateway outage, backhaul loss, interference, power recovery, credential expiry, firmware rollout traffic, and peak event bursts.
- Security boundaries: Include device identity, key rotation, certificate expiry, broker ACLs, network segmentation, and support access in the network design.
- Model limits: State which simulator assumptions were checked against measured packets, RF readings, pilot logs, installed gateway metrics, or explicit operational acceptance.
Network segmentation narrated tour
Narrated audio tour. The full transcript is below.
Play the tour to open the workbench. Pause, replay a beat, or read the full transcript below. Some situations cannot be shown by this teaching model; those beats provide captions only. The logging and review beat leaves the previous frame in place; the model does not verify real access changes.
Full transcript — Network segmentation (8 beats)
B1 — Camera foothold
You are the engineer responsible for a smart building. A camera has a weak password and shares network access with the building management server. The server holds the building's automation logic. If the camera is compromised, how far can the attacker travel toward the systems you need to protect?
Model caption: A weak-password camera is the starting compromise; the building management server holds automation logic.
B2 — Permitted crossings
Network segmentation limits the paths between groups of devices. The important question is which crossings the rules permit. In the building example, device readings should reach the gateway, the local connection to another network. They should not provide broad access to the server. Required communication still has a permitted path.
Model caption: Segmentation controls crossings: limited device-to-gateway traffic; denied device-to-core traffic. A gateway joins device links to another network.
B3 — Discovery and lateral movement
Start with the compromised camera. The attacker searches for reachable devices and services, then tries to move between devices. Movement between devices is called lateral movement. A flat network has no enforced separation between device groups, so a weak camera can provide a route toward more valuable systems.
Model caption: From the compromised camera, discovery finds reachable services; lateral movement travels between devices. Flat mode has no enforced separation.
B4 — Flat network result
Follow the flat network to the model's final recovery stage. Its reported outcome is seven compromised devices, zero blocked paths, and the building management server reached. The numbers come from preset architecture values in a teaching model. They describe the model's comparison rather than a measured incident in your building.
Model caption: Teaching model, final stage: seven compromised devices; zero blocked paths; building management server reached. Preset values, not a measured incident.
B5 — Firewall result
Keep the smart building and the same final stage, but apply the policy firewall design. Its rule is to deny crossings unless required. The outcome becomes two compromised devices and five blocked paths, with the server blocked from the attack. Required flows remain permitted. The firewall rules reduce how far the compromise can spread.
Model caption: Same model and final stage: two compromised devices; five blocked paths; server attack blocked. Required business flow remains.
B6 — VLAN misconception
A common mistake is to assume separate networks restrict access between device groups, but broad routing can still permit crossings. Now compare a design that separates devices into named networks but allows broad routing between them. At the same final stage, five devices are compromised, two paths are blocked, and access to the server remains routed. The separation fails to contain the route because the crossing is still permitted.
Model caption: Separate networks alone: five compromised devices; two blocked paths; server access routed. Broad routing still permits the crossing.
B7 — Logging and review boundary
For your building, protection comes from enforced rules. Logging crossings and reviewing rules help check the access limits as devices and access change. In the firewall comparison, the server stays protected while required communication continues. Containment means limiting the compromise's reach while preserving the flows the building needs.
Model caption: Enforced rules contain the attack while required flows continue. Logging and review confirm the boundary as access changes; the overlay illustrates that process.
B8 — Policy takeaway
Segmentation protects a building through the paths its rules stop and the necessary paths they preserve.
Model caption: Segmentation protects a building through the paths its rules stop and the necessary paths they preserve.
10.11 What This Chapter Does
This section: What This Chapter Does — This chapter orients the design sequence.
This chapter orients the design sequence. It does not replace the dedicated fundamentals, tools, methodology, assessment, or exercise chapters. Use it to understand the overall evidence loop before going deeper.
Ask the deployment question
What must the network let the IoT system do, and under what site, power, security, and operations constraints?
Compare design options
Topology, protocol, gateway placement, backhaul, segmentation, and fallback choices are compared against requirements.
Collect evidence
Paper checks, simulations, captures, surveys, pilot logs, and gateway metrics each answer different questions.
Record the basis
A decision is credible only when the assumptions, results, limits, and remaining risks are visible.
10.12 Continue to the Next Part
This section: Continue to the Next Part — Carry this evidence into Network Design: Evidence and Architecture Workflow, which begins with Build Network Evidence Route.
Carry this evidence into Network Design: Evidence and Architecture Workflow, which begins with Build Network Evidence Route.
Find help
3 reviewed answers.
Where should I start in a module?
Open the module page from the sidebar to see its chapters in order. Use the module map to return to a topic you need.
Modules and pathsReviewed
What can I try when a project does not work?
Check the symptom, then work through the diagnostic steps. Keep the error message and the smallest example that reproduces it.
When you are stuckReviewed
How do interactive examples work?
Use the interactive guide to check how examples and simulations work before changing your project.
Interactive examples guideReviewed