Design Methodology · Study deck
Network Traffic Analysis: Evidence Paths
A packet trace proves only what its capture point can see.
Blueprint Bina is your guide for this deck.
After studying this chapter
Learning objectives
You will be able to:
- Plan network traffic captures that answer a design, validation, or troubleshooting question.
- Choose capture points for device, gateway, broker, RF, backhaul, and application evidence.
- Use packet traces to review protocol timing, retransmissions, loss, joins, retries, command traffic, and maintenance events.
- Explain how encryption changes what traffic analysis can and cannot prove.
Major section
Start With the Packet You Cannot Explain
A screen at the far end cannot show whether the delay began at the device, radio hop, edge box, wide-area link, message service, or app.
- The test lead must choose views that can separate those causes.
- Traffic visibility does not grant permission to read private content or prove device trust.
- This opening does not teach every capture tool or expose encrypted content.
Major section
Capture Paths That Prove Behavior
A device capture might show DNS delay and repeated TCP SYNs.
- Network traffic analysis is strongest when it starts with a behavior to explain, then chooses the path locations that can observe that behavior.
- A gateway capture might show backhaul jitter or NAT resets.
- A cloud event stream might show that ingestion succeeded but dashboard freshness lagged.
Major section
Capture Paths That Prove Behavior (continued)
The same stale alarm can look different at a device interface, an 802.15.4 sniffer, a LoRaWAN gateway, an MQTT broker, a cloud ingress point, and an application log.
- A broker log might show session expiry, QoS acknowledgements, or a retained-message surprise.
- For IoT design work, the goal is not to collect every packet.
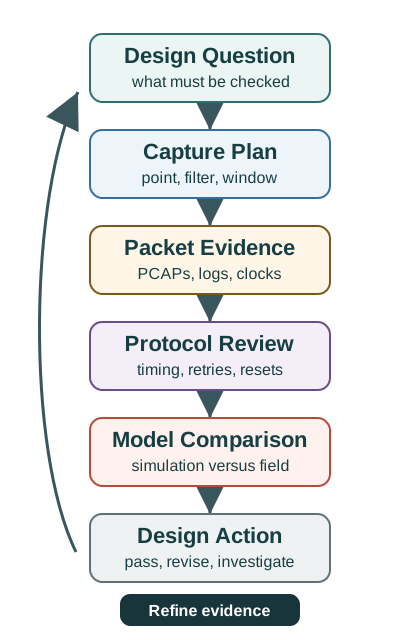
- Packet evidence supports protocol review and model comparison before the team decides to pass, revise, or investigate.
Major section
Build Readable Trace Bundles
A useful trace bundle includes the PCAP or flow export, the capture command, interface, channel, filter, time zone, clock source, device identifiers, software versions, scenario notes, and the logs needed for correlation.
- Wireshark is good for interactive protocol review. Tshark is better for repeatable extraction in a test script.
- Nordic nRF Sniffer, TI SmartRF Packet Sniffer, Ubertooth, or an 802.15.4 capture dongle can expose BLE, Thread, Zigbee, or raw link behavior that an IP capture misses.
- ChirpStack, The Things Stack, or packet-forwarder logs can expose LoRaWAN join attempts, RSSI/SNR, frame counters, gateway id, and downlink timing when payloads stay encrypted.
Major section
Trace Visibility Has Limits
Monitor-mode radios may miss frequency hops or channels outside the selected band.
- A TCP retransmission shows transport recovery, but the cause may be RF loss, buffer pressure, roaming, firewall state, broker overload, or backhaul jitter.
- The under-the-hood skill is separating transport evidence from application meaning.
- Packet-forwarder logs may round or normalize timestamps.
Major section
Trace Visibility Has Limits (continued)
A missing packet in one capture can mean the packet never existed, the capture point missed the channel, the filter was too narrow, or the clock alignment points to the wrong event window.
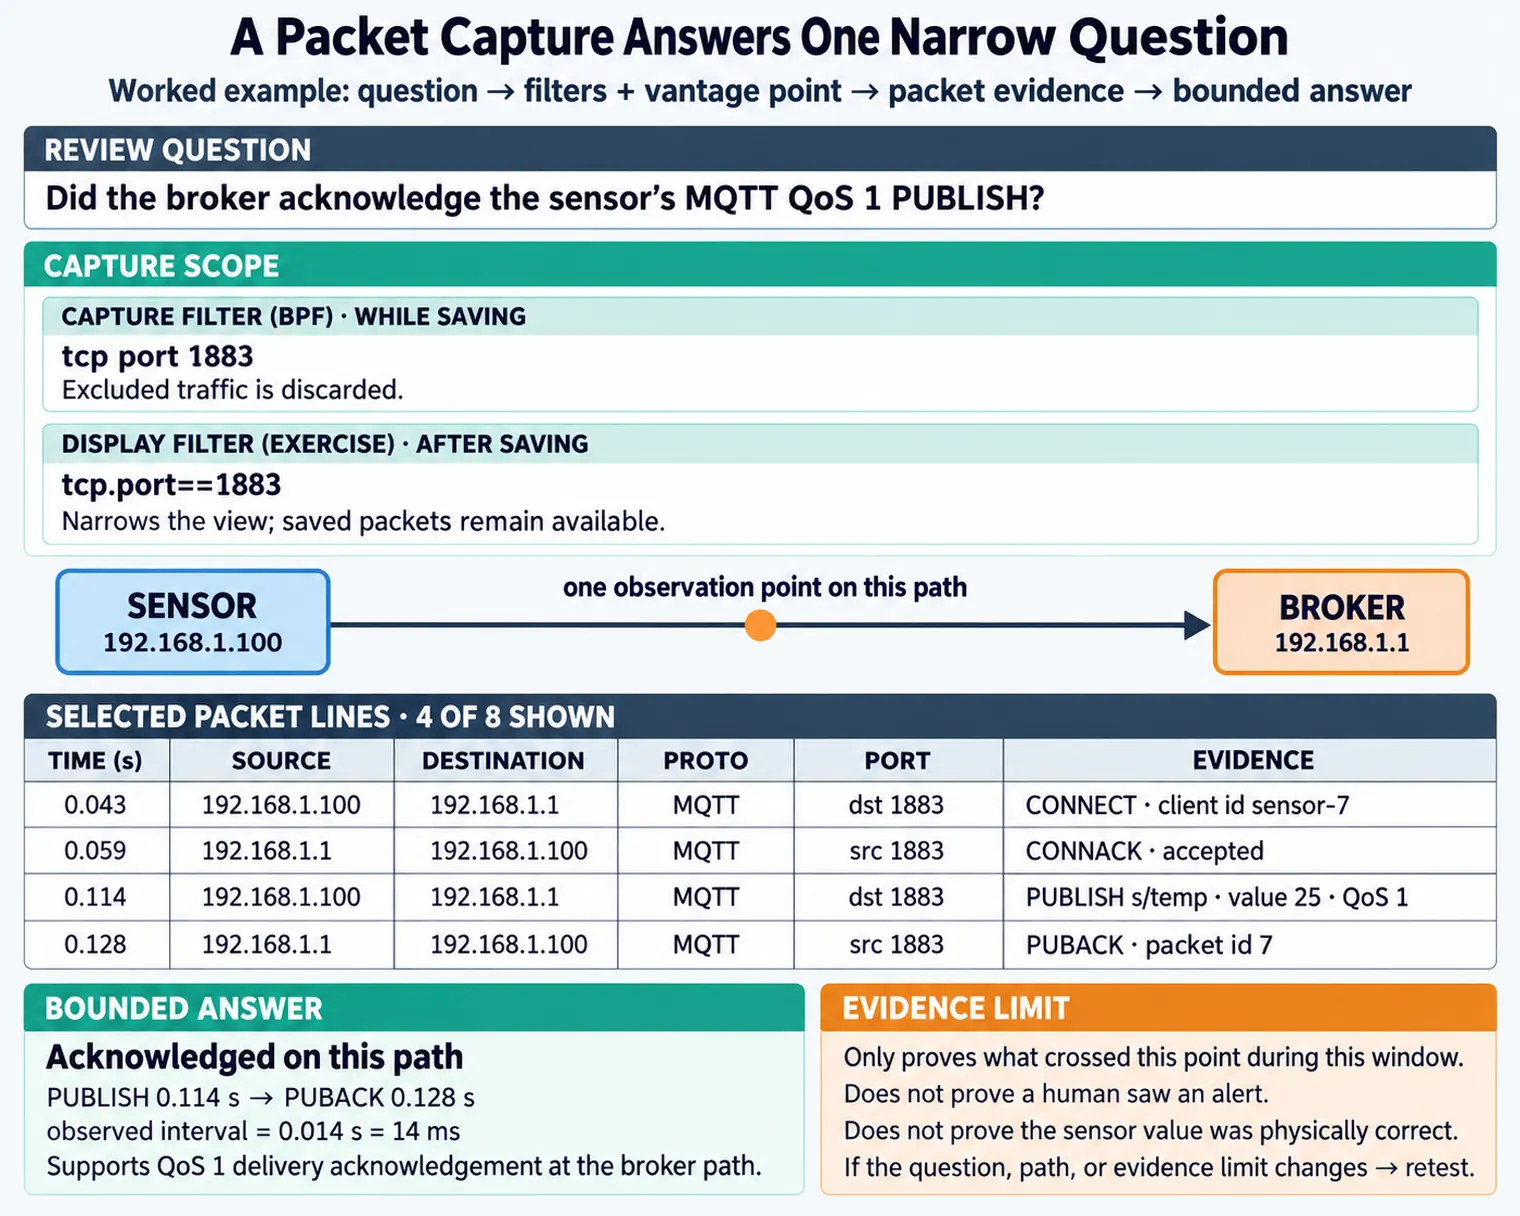
- MQTT QoS 1 PUBACK timing can show delivery acknowledgement at the broker path, but it does not prove a human saw an alert.
- A CoAP ACK can prove message exchange at the protocol layer, but it does not prove a sensor value was physically correct.
- LoRaWAN frame counters and RSSI/SNR can show link behavior, but payload meaning still needs device, network-server, or application context.
Major section
Trace Visibility Has Limits (continued)
BLE supervision timeouts, Thread parent changes, Wi-Fi roaming, and cellular reconnects each leave different evidence trails, so the capture point must match the mechanism under review.
- Network-interface offload can make local checksum fields look wrong even when transmitted packets were valid.
- Broker logs may show accepted sessions but not every dropped network packet.
- Flow logs aggregate events and can hide short retransmission bursts.
Major section
Capture Planning
A capture without a question often becomes a large file that nobody can review.
- The behavior or decision being checked.
- Different points can see different symptoms and hide different details.
- Correlation fails when traces, logs, and simulations use inconsistent time references.
- Payload sensitivity, decryption policy, redaction plan, key handling, and retention limits.
Major section
Packet Captures Hold Sensitive Data
They may include tokens, device IDs, locations, topic names, DNS names, certificate details, or plaintext payloads in development networks.
- The plan in Figure: A capture plan keeps the trace tied to scopes an MQTT receipt trace; check filters and limits because packets may hold private data.
- Scope sets filters and endpoints before packets reveal sequences, timing, and retries.
- The evidence limit constrains the decision; changes to the question, path, or that limit require a retest.
Deck summary
Key takeaways
A screen at the far end cannot show whether the delay began at the device, radio hop, edge box, wide-area link, message service, or app.
- A device capture might show DNS delay and repeated TCP SYNs.
- The same stale alarm can look different at a device interface, an 802.15.4 sniffer, a LoRaWAN gateway, an MQTT broker, a cloud ingress point, and an application log.
- A useful trace bundle includes the PCAP or flow export, the capture command, interface, channel, filter, time zone, clock source, device identifiers, software versions, scenario notes, and the logs needed for correlation.
Retrieval practice
Recall check 1 of 4

Blueprint Bina says: answer from memory, then check your reasoning.
Q1A device says it sent an alarm, but the broker has no record. Which trace comparison best tests the gap?
Show answer
Answer: C Aligned records locate where delivery stopped and whether retries occurred.
Retrieval practice
Recall checks 2–3 of 4
Blueprint Bina says: answer from memory, then check your reasoning.
Q2A cloud service ingests an alarm, but the dashboard remains stale. Where should the investigator extend the evidence path?
Show answer
Answer: D Ingestion success does not prove dashboard freshness; the chapter separates these observation points.
Q3Another engineer must reproduce a gateway traffic analysis. What should accompany the capture file?
Show answer
Answer: C The bundle preserves how the capture and summary were produced.
Retrieval practice
Recall check 4 of 4
Blueprint Bina says: answer from memory, then check your reasoning.
Q4A dashboard is stale after a gateway restart. Which packet evidence helps separate retry delay from missing data?
Show answer
Answer: D The capture and logs expose the timing path through recovery.
Print reference
Answers
Answer key.
- C · Aligned records locate where delivery stopped and whether retries occurred.
- D · Ingestion success does not prove dashboard freshness; the chapter separates these observation points.
- C · The bundle preserves how the capture and summary were produced.
- D · The capture and logs expose the timing path through recovery.